When a compromised package or action runs in CI, you need to know what it could reach. Depi now tracks the secrets and permissions of the GitHub workflows an incident touches in order to facilitate incident response.
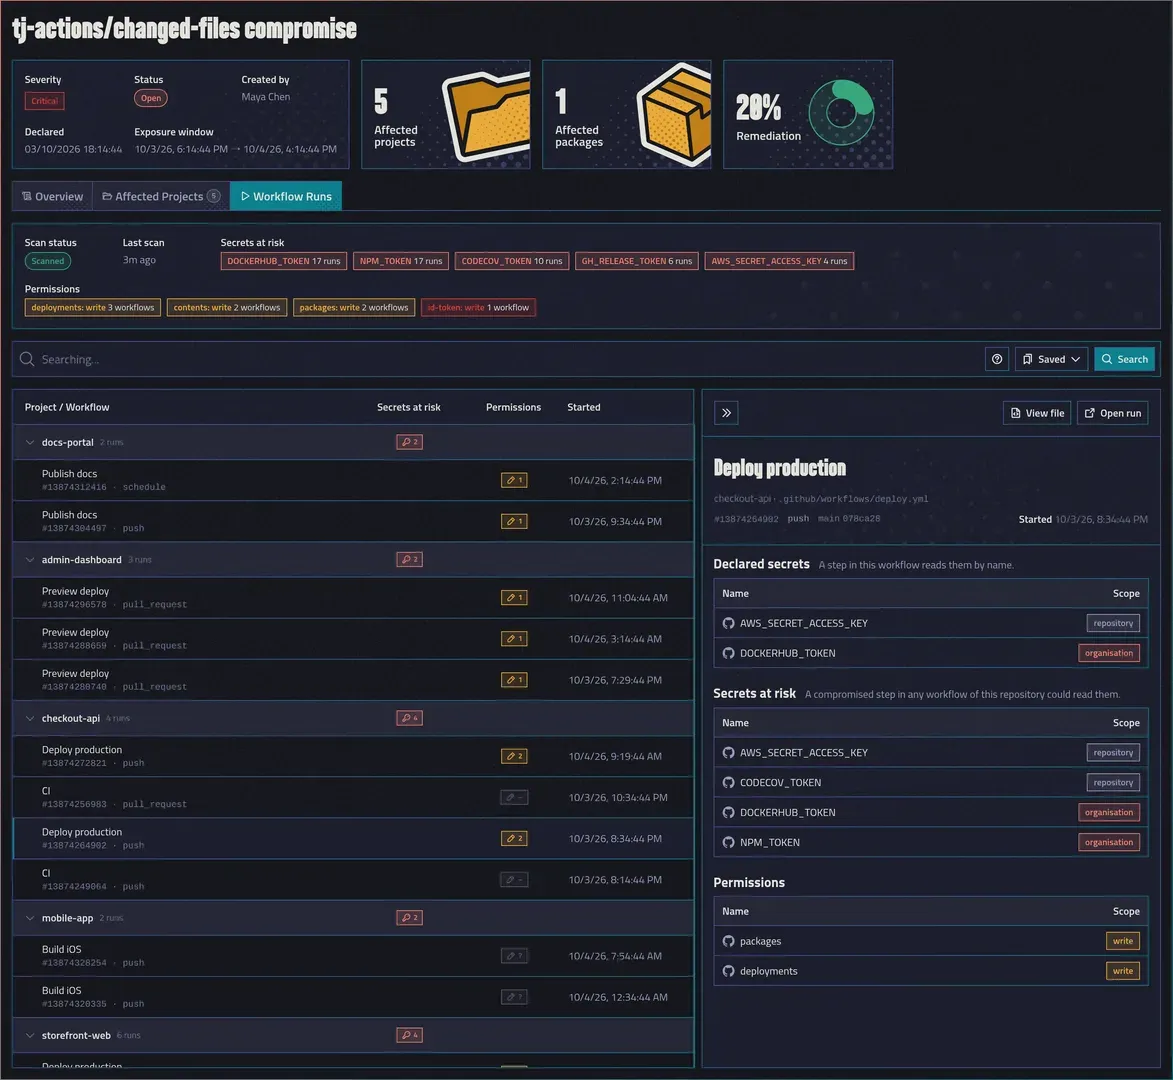
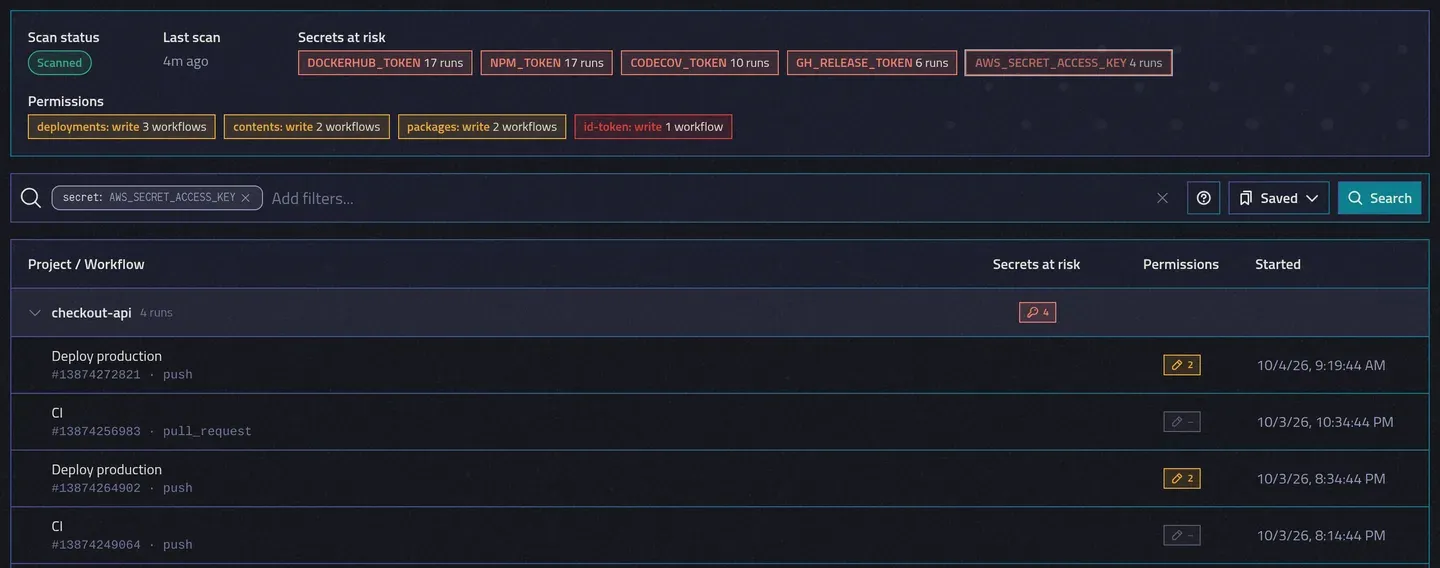
Depi looks at every workflow that ran during the incident window and matches it against the project’s secrets and access. The new Workflow runs tab shows the result: what may be compromised, and what you may need to rotate.
Declared secrets and secrets at risk
Depi keeps two lists apart:
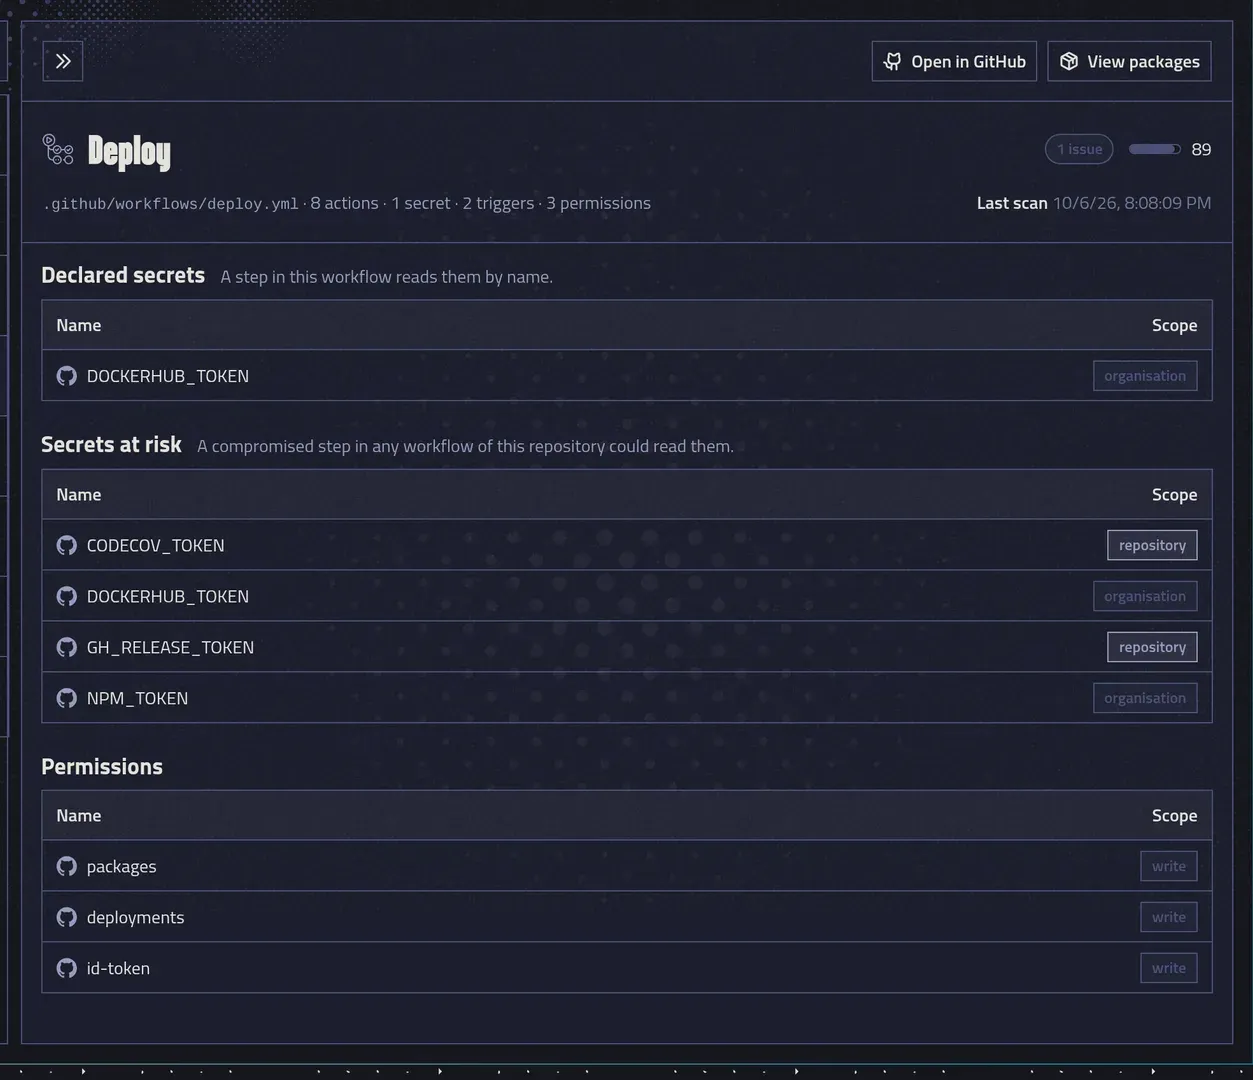
- Declared secrets: a step in this workflow explicitly reads them by name.
- Secrets at risk: all the secrets that the workflow can read.
In this example, checkout-api still uses a long-lived AWS key, and four of its runs could read it:
Pipeline secrets
Depi re-uses the same logic in the reworked Project pipelines view, which should bring more clarity on what secrets and permissions a pipeline has.