As part of our deepened partnership with Aikido, Depi now checks the packages you use against its malware feed. When malwares are detected as installed or reachable, Depi will automatically create a managed incident for you. As new malwares get detected, the incident gets updated, and we record when the public registries pull them.
Depi Managed incidents
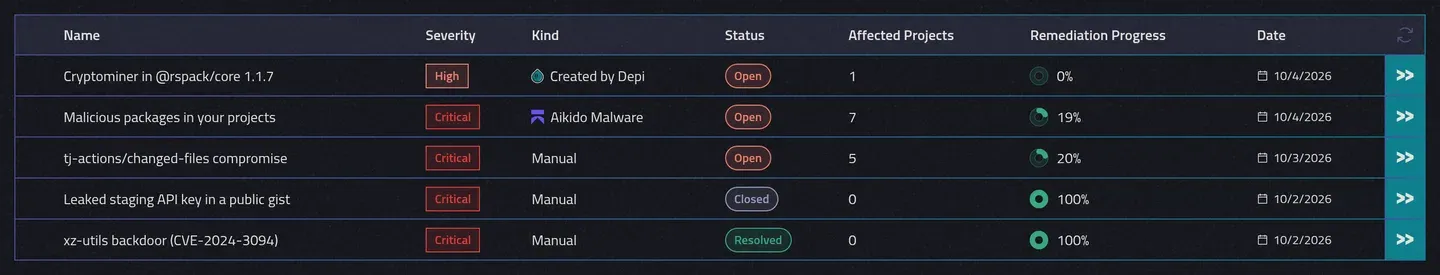
Incidents marked “Created by Depi” are the ones our security researchers create manually to protect all Depi users. They will be updated as the new supply chain attack campaign expands, and as the public registries pull the malicious versions. You can still declare your own incidents, and Depi will keep them separate.
Aikido Malware incidents are automatically created when a malware is detected as being used, or reachable, in your projects.
Pulled versions
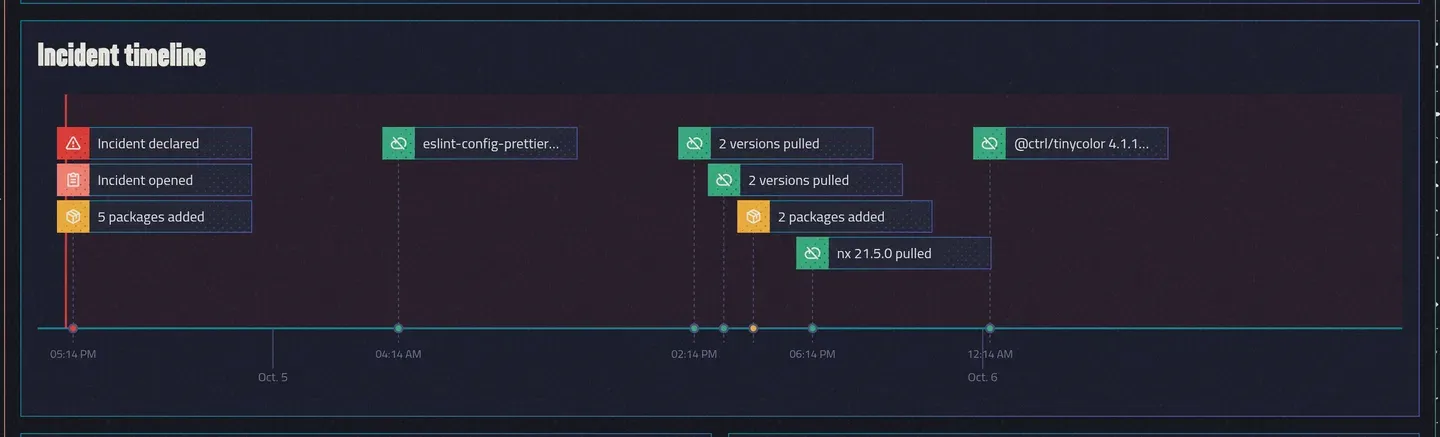
When a malware gets pulled out of the public registry, it is no longer installable but might have been installed. We recommend the affected projects view to see which projects are affected and could have installed the malicious version.
The timeline records when each package joined the incident and when the registry pulled each version.
Get alerted
With the notifications feature, you can then send incidents updates to Slack or to your on-call tool through a notification channel. Helping you stay on top of the incident and react quickly.


