We’ve added a new section called “Threat Intel” to the app which gives you direct access to Depi’s Threat Intel. You can now check packages without having to use the API.
Check your packages
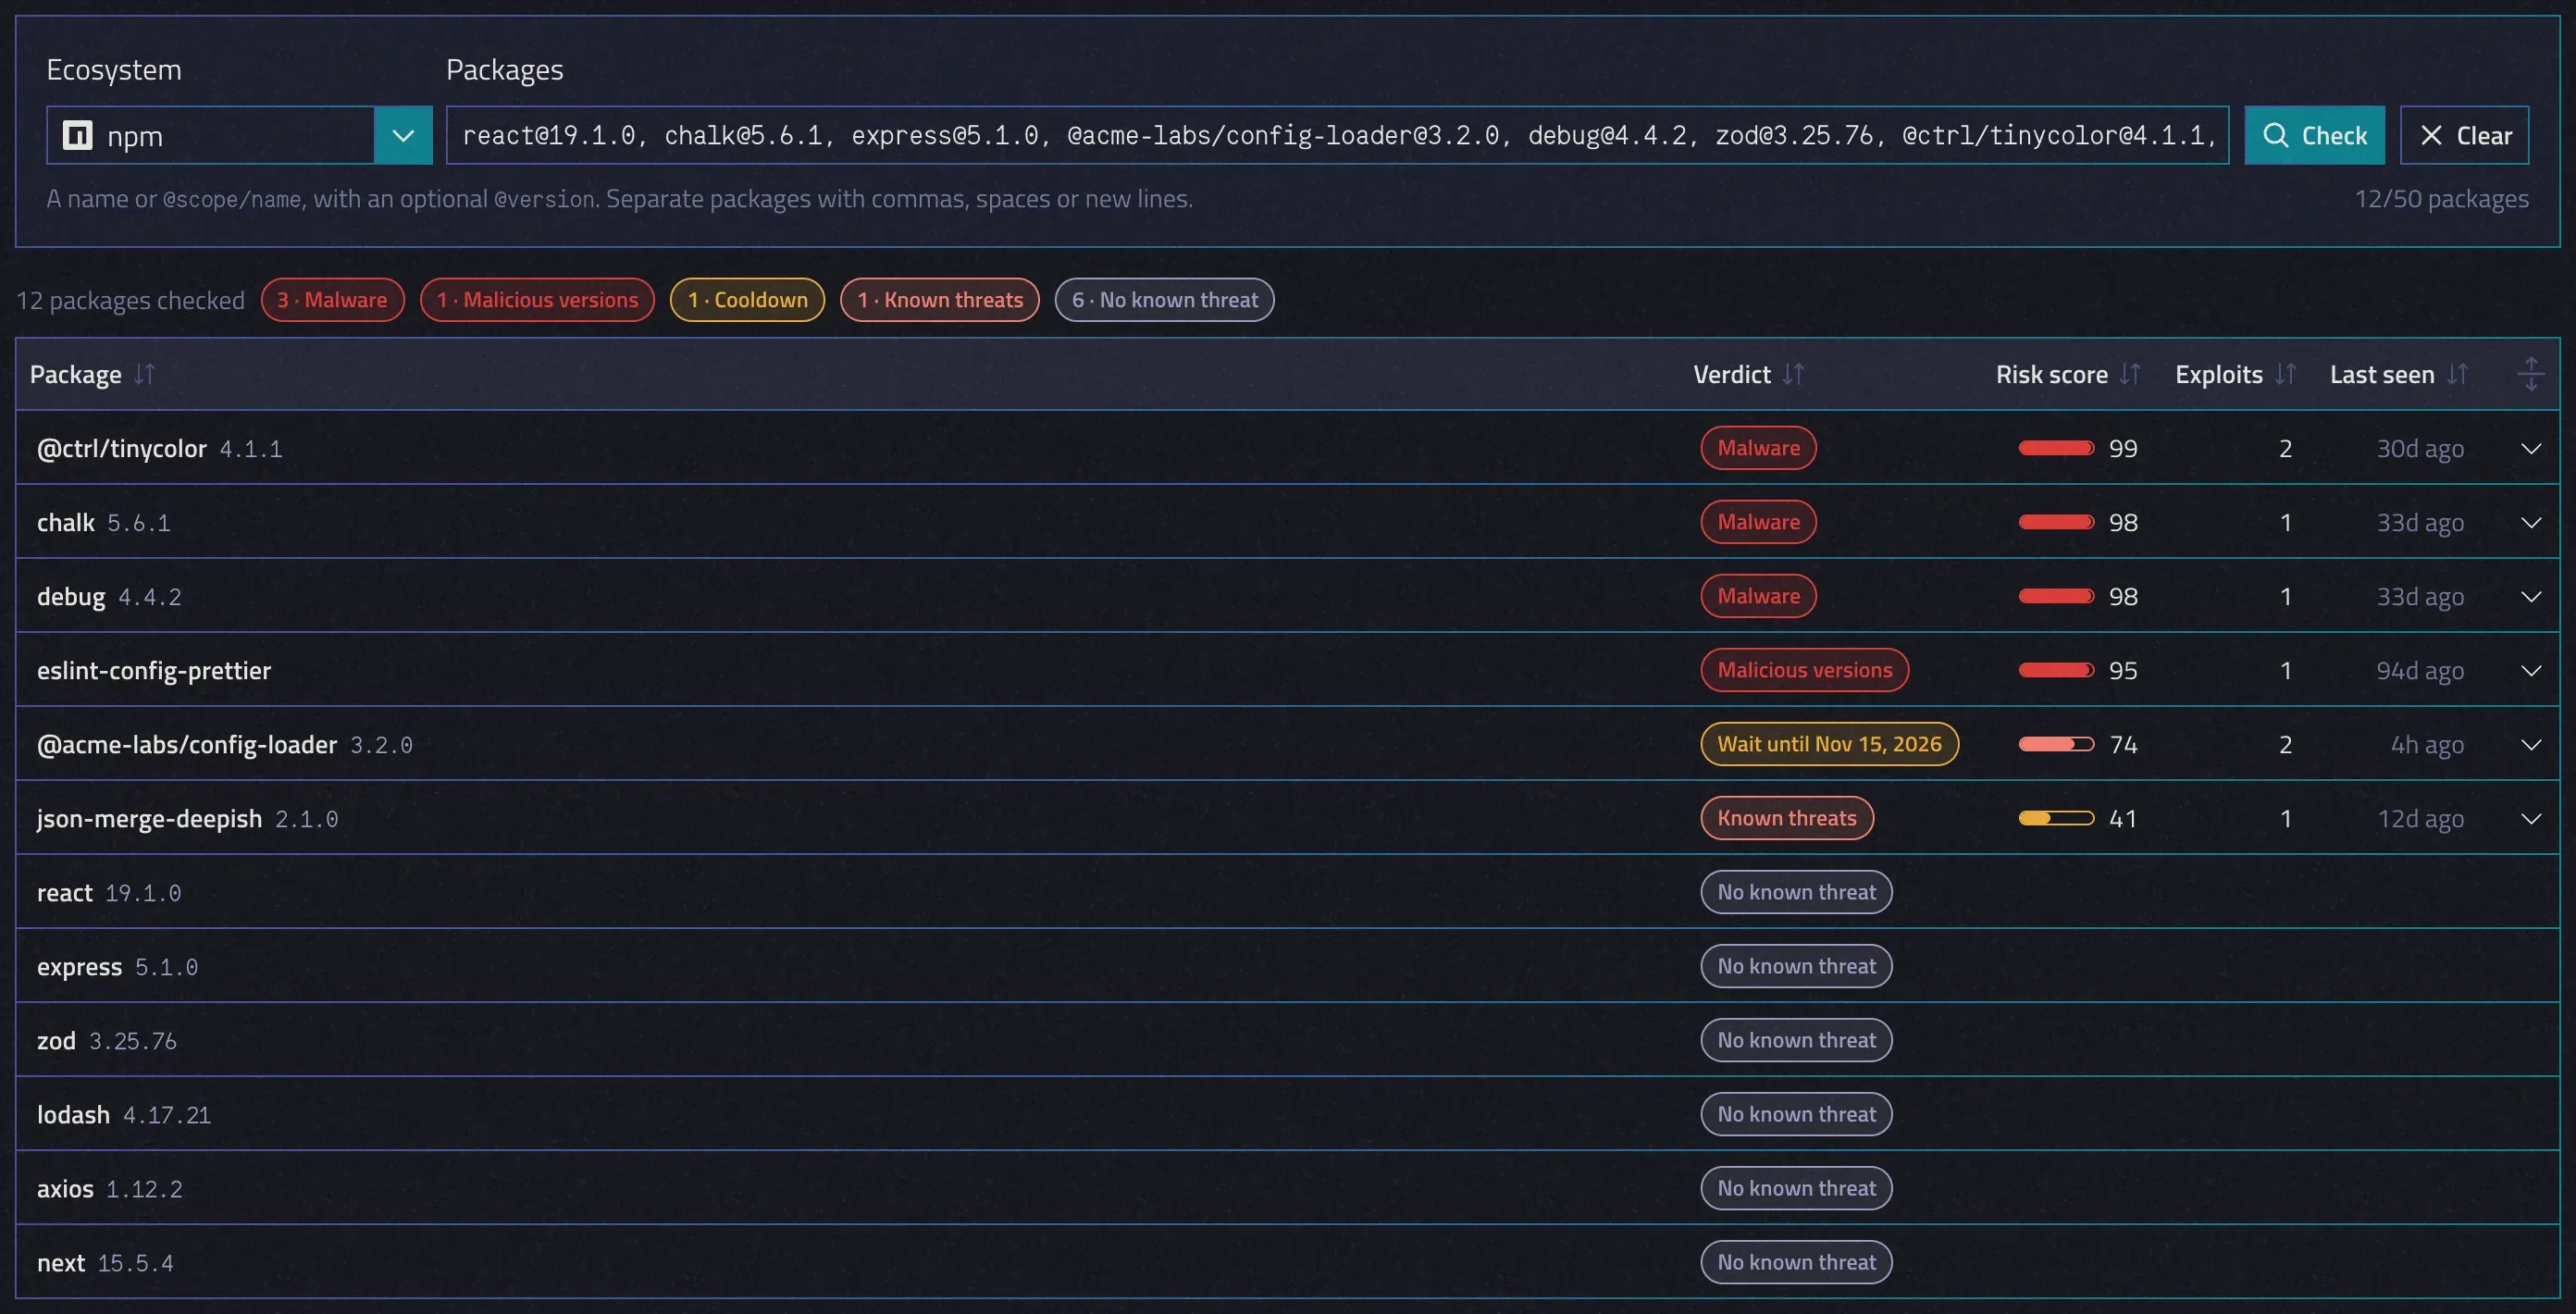
You can directly paste a list straight from a file: commas, spaces and new lines all separate packages definitions. You can mix package names with versions or just package names. For example:
chalk@5.6.1, debug@4.4.2, @ctrl/tinycolor@4.1.1, eslint-config-prettierEach package gets one verdict:
- Malware: the version you asked for is malware.
- Malicious versions: you gave no version, and some releases are malware.
- Wait until: the package has known exploits, and your organisation’s cooldown policy holds it until this date.
- Known threats: the package has known exploits, but your cooldown policy lets you install it now.
- No known threat: we know of no threat for this package.
The worst verdicts come first, with the risk score, the exploit count and when we last saw the threat.
See why
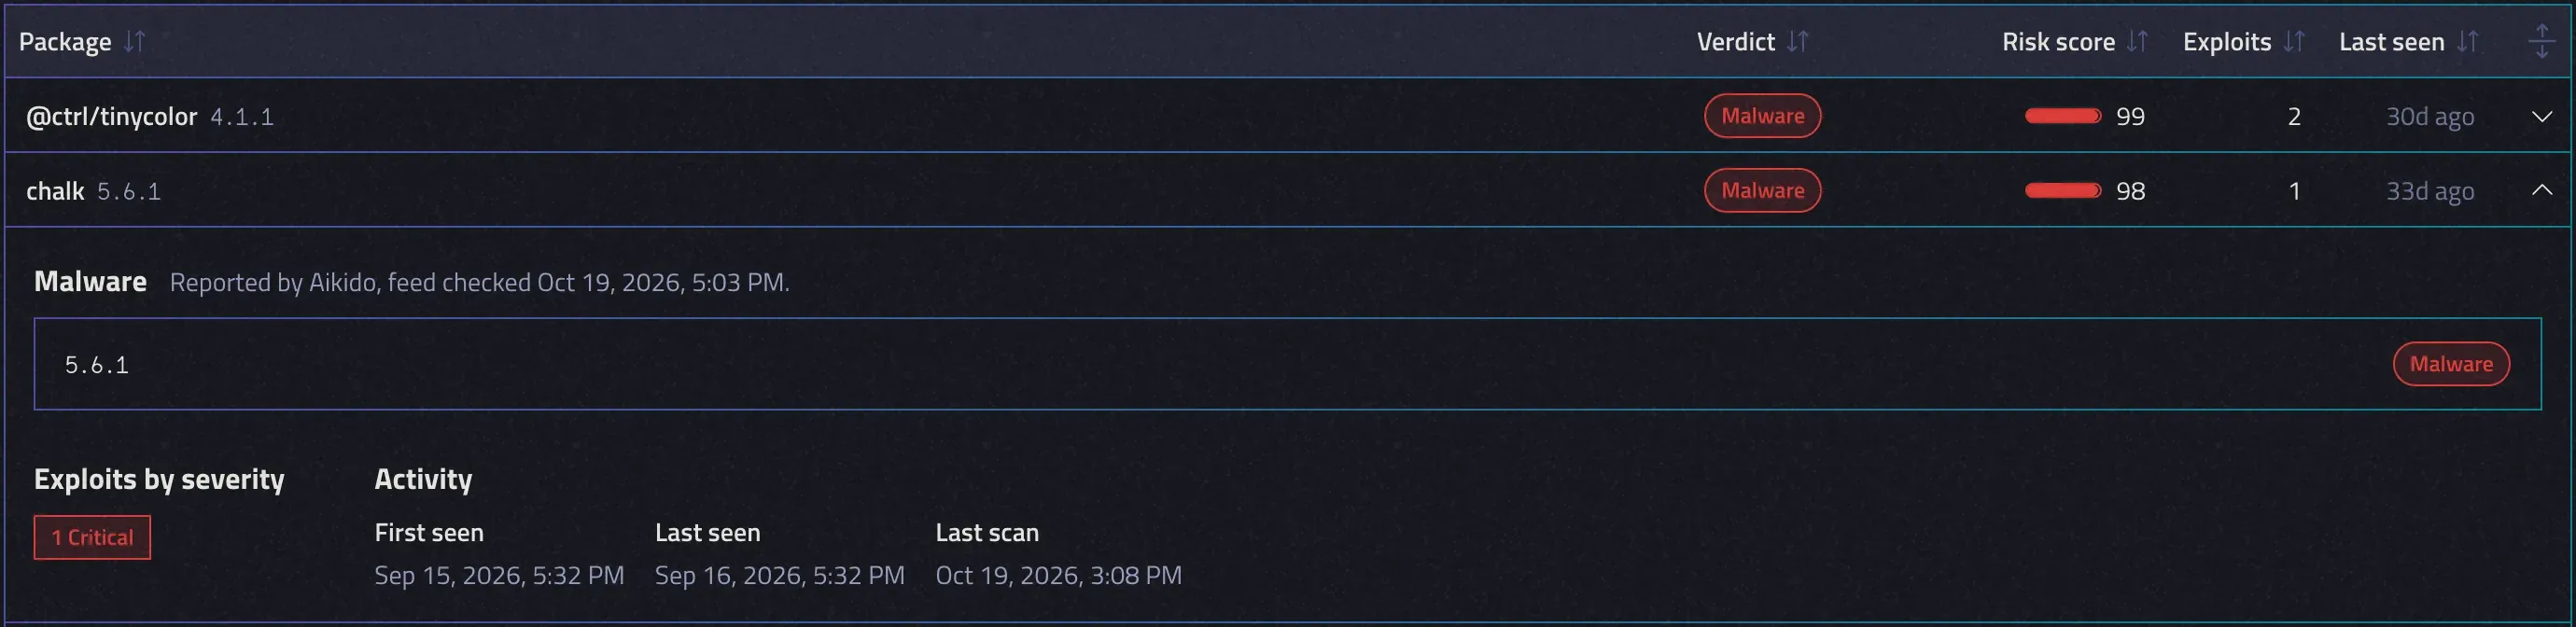
Expand a row to see the finding. In this example, chalk 5.6.1 and @ctrl/tinycolor 4.1.1 are
publicly documented cases from the September 2025 npm compromises.